Written by: Xiaobing, Shenchao TechFlow
In the early hours of October 30, 2026, Binance's hot wallets on 9 chains were breached simultaneously, with over 6.26 billion USD transferred out on-chain.
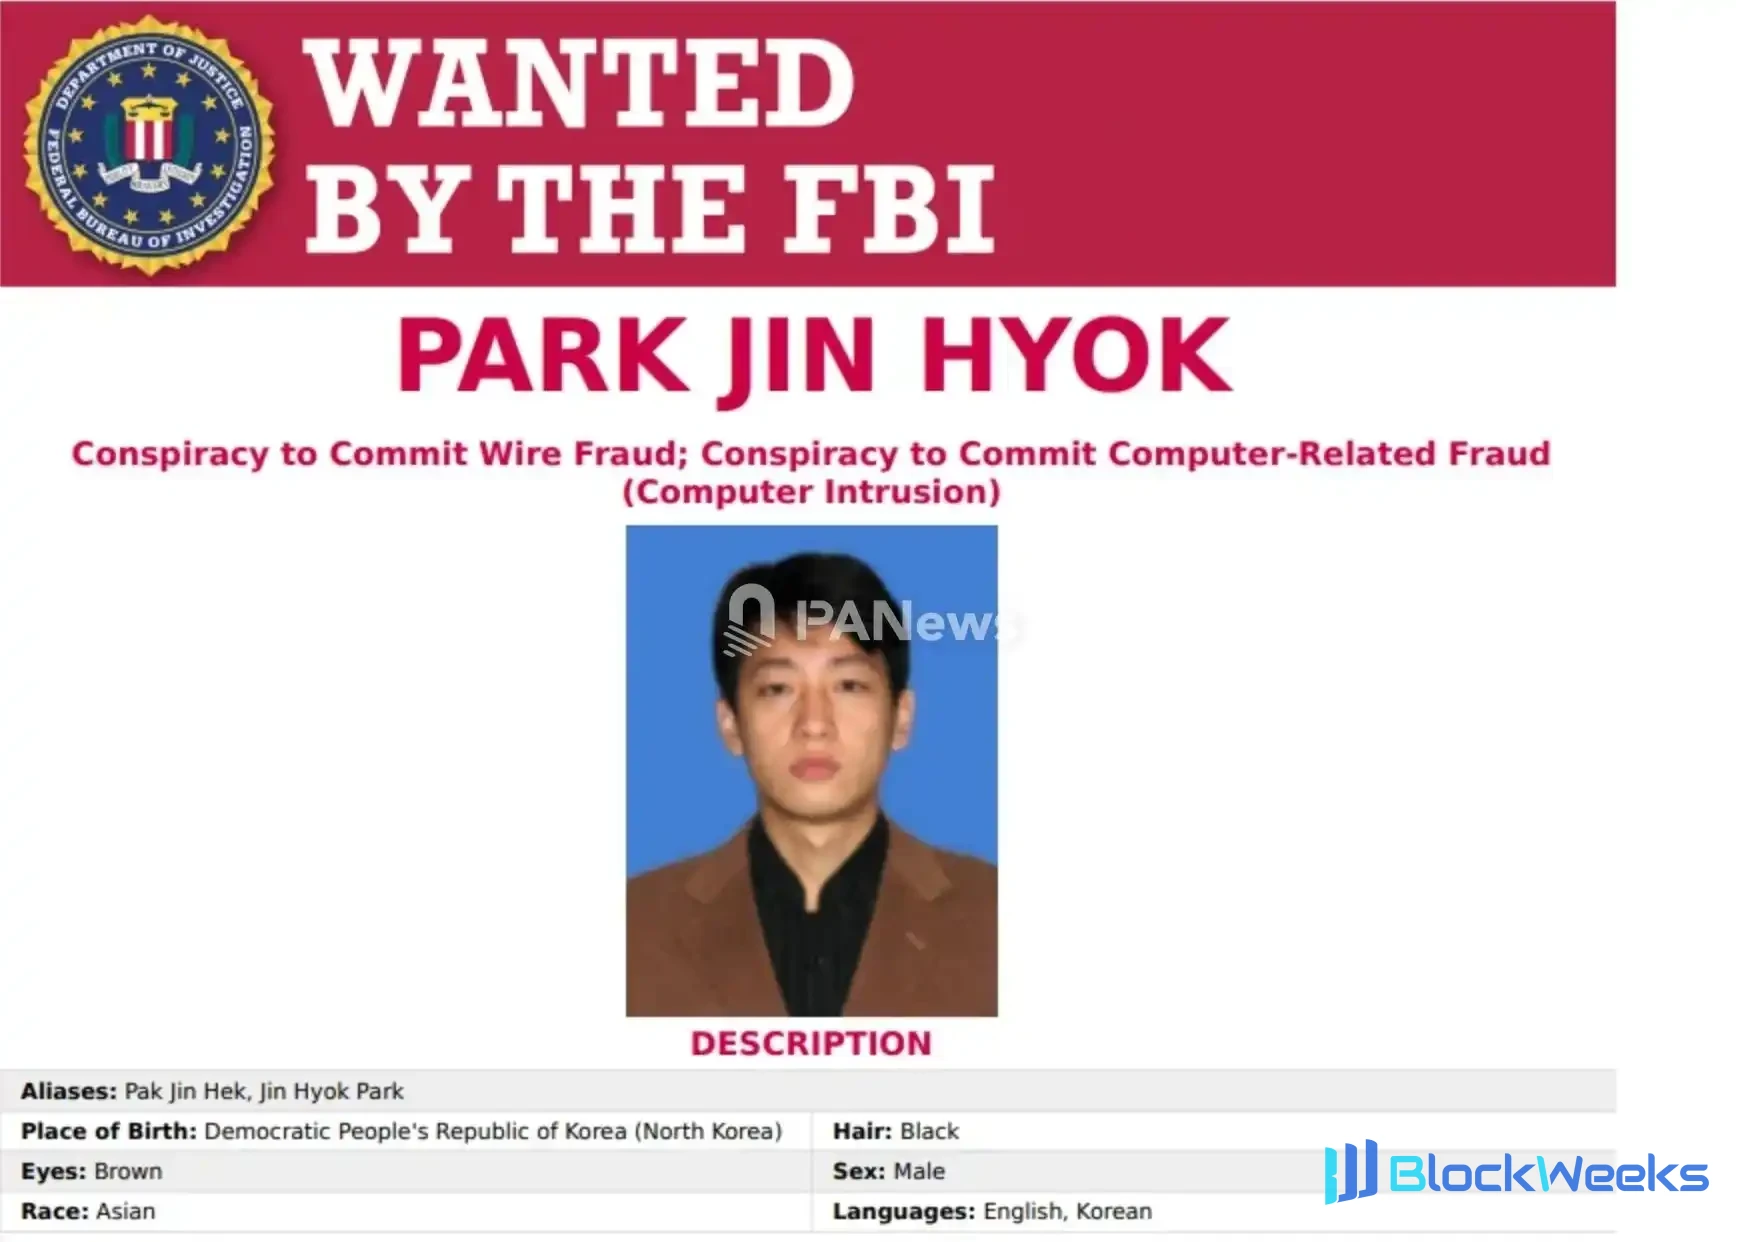
On October 31, it was announced that the U.S. Federal Bureau of Investigation (FBI) announced that North Korean hacker groups were involved in the Binance theft, and Trump stated that if it is confirmed to be North Korea's doing, the U.S. will negotiate with North Korea.
A country has turned the entire crypto industry into an ATM.
According to Shenchao TechFlow statistics, between 2017 and 2026, hackers associated with Lazarus and North Korea were involved in a total of 37 crypto theft cases, with an estimated total value of approximately 11.817 billion USD.
From starting with the 2017 attack on South Korean exchange Bithumb, stealing 7 million USD, to Binance evaporating billions overnight, how did North Korea, considered to have a closed network, go from a marginal player in the cyber battlefield to the top predator in the crypto world in less than a decade?
One PDF, Six Hundred Million Dollars
In early 2022, a senior engineer at Sky Mavis, the parent company of crypto game Axie Infinity, received a LinkedIn message from someone claiming to be a recruiter at a certain company, offering a highly attractive compensation package.
The engineer went through multiple rounds of interviews, and everything seemed legitimate. Ultimately, he received an offer letter in PDF format. The moment he opened the file, spyware silently infiltrated Sky Mavis's internal systems.
Axie Infinity's Ronin Bridge uses a proof-of-authority mechanism with 9 validator nodes, requiring 5 node signatures to approve withdrawals. The attackers penetrated Sky Mavis's IT infrastructure through the infected engineer's computer and obtained the keys of 4 validators. The 5th signature came from a forgotten vulnerability: in November 2021, Sky Mavis had requested Axie DAO to help sign during peak transaction load, and this temporary authorization had been discontinued in December, but access permissions were never revoked.
In March 2022, 620 million USD disappeared from Ronin Bridge. A month later, the FBI attributed the attack to North Korea's Lazarus Group.
A fake offer, a forgotten authorization, six hundred million dollars stolen.
The Ronin script has been repeatedly replayed since then, but the attackers' methods have evolved.
In June 2022, Harmony Horizon Bridge fell, and 100 million USD was transferred away. The attackers disguised themselves as blockchain developers and obtained system permissions as insiders. In 2023, Atomic Wallet, Alphapo, CoinsPaid, and Stake.com fell one after another, with cumulative losses exceeding 238 million USD. By July 2024, Indian exchange WazirX was breached for 235 million USD.
Each attack used a different method, but the logic behind them is strikingly consistent: find a person, deceive that person, use that person to open a door.
In February 2025, they pushed this methodology to a new height.
Bybit's cold wallet was drained of 1.5 billion USD. Paradigm security researcher samczsun's post-mortem showed that the attackers did not directly attack Bybit, but infiltrated the infrastructure of its multisig wallet service provider Safe{Wallet}, planting malicious code there and precisely targeting Bybit's cold wallet signing process. This means that even if Bybit's own security measures were impeccable, as long as the upstream supply chain was breached, all defenses were rendered useless.
Eight months later, Binance became the latest prey.
Binance's post-incident investigation results showed that a laptop of an operations engineer was compromised, and the attackers used it to infiltrate internal systems and used EIP-7702 to make the hot wallet sign a delegation authorization. Shenyu deconstructed the logic of the attack contract in an on-chain post-mortem: "The attacker's program recognizes only one master and does only one thing: transfer money."
From Ronin to Bybit to Binance, the scale of attacks jumped from 600 million to 1.5 billion, and then to 6.2 billion. Each time was a victory for social engineering, and each time started with one person.
Your Colleague Might Be North Korean
If Lazarus's external attacks are "breaking down the door," then the infiltration of North Korean IT workers is "entering the house through the front door."
In October 2024, CoinDesk published an investigative report that shocked the industry. Reporters tracked blockchain payment records and internal leads and found that more than 24 crypto companies had unknowingly hired North Korean IT workers, with at least 12 companies confirming they had found suspected North Korean employees on their staff lists. Named projects included Cosmos Hub, Injective, ZeroLend, Fantom, Sushi, Yearn Finance, and Truflation.
MetaMask security researcher Taylor Monahan revealed that at least 40 DeFi protocols had hired North Korean IT workers during their development history, spanning as long as seven years.
These people passed screening using forged passports, visas, and carefully fabricated resumes, submitting applications on Telegram, Discord, and Indeed. They targeted startup teams with loose hiring processes and crypto-denominated salaries, and almost never turned on their cameras while working remotely. According to United Nations estimates, North Korean IT workers earn up to 600 million USD annually for the regime, of which individuals can keep only 10% to 30%.
In March 2024, the Munchables incident provided a textbook case.
This NFT game based on the Blast chain hired a developer under the pseudonym "Werewolves0943." On-chain investigator ZachXBT traced and found that this developer was a North Korean spy who used development permissions to extract 17,400 ETH from the project, worth approximately 62 million USD.
The twist in the story is that, under pressure from Blast founder Pacman and the community, the developer handed over all private keys within 8 hours and fully refunded the stolen funds. No one knows why he returned them. One guess is that after being exposed, continuing to hold the stolen funds would only bring greater trouble.
But Sushi's experience was not so lucky.
In September 2021, the Sushi/MISO platform was hacked for approximately 3 million USD. Post-incident investigation found that two former contractors under the pseudonyms "Anthony Keller" and "Sava Grujic" retained access to the codebase after being dismissed. Sushi later also hired another suspected North Korean contractor, "Gary Lee." In 2023, Truflation founder Stefan Rust discovered that 5 members of his team were suspected North Korean workers, more than one-third of all employees. The company subsequently suffered a private key leak attack of approximately 5 million USD.
CrowdStrike data shows that North Korean IT workers infiltrated more than 320 companies within 12 months, a year-over-year increase of about 220%.
They use fake identities, hire people locally in the United States to set up multiple computers for centralized remote work to fake their geographic location, and use generative AI to handle video interviews.
Security company KnowBe4 even found that it had also been duped: an "employee" who joined through the normal recruitment process immediately began deploying malware after starting work.
Unable to Say a Single Bad Word About Kim Jong Un
What kind of people are North Korean hackers?
In August 2026, a Korean-American journalist, with the assistance of MetaMask security researcher Taylor Monahan, SEAL Alliance's Nick Bax, and Ump Labs, disguised as a recruiter "Sophie Wang" and conducted a video interview with a suspected North Korean state-level hacker.
This job applicant called himself "Justin Lim" and claimed to live in Long Beach, California, but his accent was judged to be Korean. On-chain clues and identity data indicate that his actual location is very likely Vladivostok, Russia, and he stole approximately $2.7 million from MetaPlay in 2022.

During the interview, he demonstrated considerable technical ability: he explained how to fork the Velas network and get The Graph running compatibly, and when encountering the unfamiliar OpenSea Seaport protocol and Uniswap v4, he would pull up the documentation on the spot and analyze it.
When the interviewer mentioned that North Korea stole $1.5 billion from Bybit, he showed the only smile of the entire interview.
The last question ended everything. The interviewer asked him to say something negative about Kim Jong-un. After a silence, he exited Zoom. He then cited "unstable internet" and asked to continue communicating via Discord or Telegram. When pressed again, he replied only: "I don't know much about this person."
In North Korea, publicly criticizing the supreme leader can result in three generations being sent to political prison camps. This test was later widely recommended by the security community as a recruiting screening method: require candidates to make a negative comment about Kim Jong-un, and almost all North Korean developers will choose to avoid it.
Secret War
North Korea's cyberattack capabilities were not built overnight.
According to defector Jang Se-yul's disclosure to Business Insider, North Korea's cyber warfare program can be traced back to the 1980s, with the internal codename "Secret War." The Kim regime realized early on that, given that its conventional military power is far inferior to that of the U.S.-South Korea combined forces, cyber operations are the lowest-cost, highest-return asymmetric weapon.
Training a North Korean hacker takes about nine years. The starting point is Kim Chaek University of Technology (formerly the University of Automation), which admits 100 people each year from about 5,000 applicants. The screening criteria first look at political background; North Korea's "songbun" system divides citizens into three main classes and 56 subcategories, recorded in household registration files. Trainees take six 90-minute classes a day, study programming languages and operating systems, delve deeply into Windows architecture, and are required to write malware independently without relying on ready-made tools.
After graduation, hackers are assigned to action groups targeting countries and embedded overseas under the identity of legitimate corporate employees for about two years, learning the local language and culture. The pay is extremely generous: up to $2,000 per month, twice the salary of a North Korean ambassador. Rewards also include an apartment in Pyongyang of more than 185 square meters and the right to move the whole family to the capital.
"The cost of training hackers is extremely low," Jang Se-yul said. "That is why even a poor country can invest heavily in this field."
In his view, the cyber threat is more direct and more dangerous than the nuclear threat: "This is a war that does not require firing a gun."
Ghost Empire
The U.S. Department of the Treasury sanctioned three entities in 2019—Lazarus Group, BlueNoroff, and Andariel—and stated that all of them are controlled by North Korea's Reconnaissance General Bureau (RGB), but the name "Lazarus" is actually just the outside world's collective term for a vast state-level cyberattack system.
In an analysis published after the Bybit incident, Paradigm security researcher samczsun mapped out this intricate organizational network:
TraderTraitor: The big-game hunter. Specializing in exchanges, custodians, and wallet systems, skilled in spear-phishing and fake job opportunities; Ronin, WazirX, and Bybit all came from this team. They usually do not use zero-day vulnerabilities, but instead pry systems open by manipulating "people."
AppleJeus (Citrine Sleet): The supply-chain assassin. Develops trojanized software around crypto scenarios; the 2024 infiltration of Radiant Capital is its signature work. They also used the Chromium zero-day vulnerability CVE-2024-7971 to deploy the FudModule Rootkit.
BlueNoroff (Sapphire Sleet): The financial hunter. In its early days it attacked banks and SWIFT systems, and in 2016 it nearly made off with $1 billion from the Bangladesh central bank (actually obtaining $81 million). It has now fully shifted to the crypto and VC sectors.
Famous Chollima: The infiltrator. It joins tech and crypto companies through fake identities, creating internal penetration capability. The 320 infiltrated companies tracked by CrowdStrike are mainly the work of this team.
DangerousPassword: Low-cost, broad-net casting. Phishing emails and fake video call apps; the methods are simple but win through volume.
There is extensive overlap in members, tools, and infrastructure among these branches, and different security agencies give them different names. Diamond Sleet, UNC4899, Contagious Interview, Wagemole.
The same adversary, a dozen names, different masks.
Asymmetric Warfare
After the Binance incident, Musk posted on X: "Everyday is Zeroday."
This is not rhetoric. A special research report released by Microsoft's threat intelligence department shows that among the eight major active North Korean hacker groups, three have already completed deep integration of AI tools with daily attack workflows, reaching the highest level in Microsoft's maturity model for AI application in cyber threats.
AI's involvement is no longer confined to peripheral experiments; it now fully covers the entire chain of early reconnaissance, social engineering phishing, identity disguise, malware writing, and even software supply chain poisoning. In other words, the phishing emails, fake resumes, and malicious code that once required weeks of preparation can now be generated in bulk and automatically iterated.
The attacker only needs to find one vulnerability; the defender must protect against all vulnerabilities. This is an asymmetric war.
From Bithumb's $7 million to Ronin's $620 million, from Bybit's $1.5 billion to Binance's $6.2 billion, the scale of attacks has grown exponentially. At the other end of this curve is a country with a per capita GDP of less than $2,000, a group of young people who began nine years of training at age 17, and a state machine that has served "Secret War" for forty years.
The crypto industry must face a fact: standing on the opposite side is the entire cyber warfare power of a nuclear-armed state, and this adversary is becoming stronger and stronger.